

|
시장보고서
상품코드
2124550
소프트웨어 구성 분석 : 시장 점유율 분석, 업계 동향과 통계, 성장 예측(2026-2031년)Software Composition Analysis - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2026 - 2031) |
||||||
 Mordor Intelligence
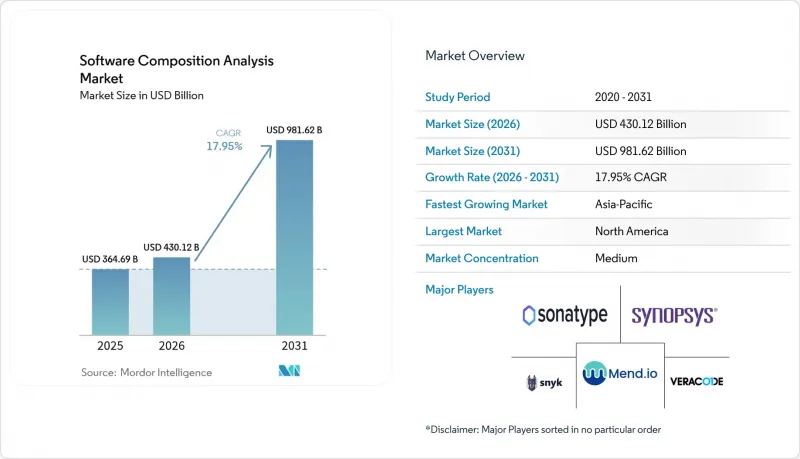
에 의하면, 소프트웨어 구성 분석 시장 규모는 2025년에 3,646억 9,000만 달러로 평가되었고, 2026년 4,301억 2,000만 달러에서 2031년까지 9,816억 2,000만 달러에 이를 것으로 예측되며, 예측 기간(2026-2031년) CAGR은 17.95%를 기록할 전망입니다.
본 보고서는 구성 요소(솔루션, 서비스), 도입 형태(클라우드, On-Premise, 하이브리드), 조직 규모(대기업, 중소기업), 업종(IT 및 통신, 은행, 금융서비스 및 보험(BFSI), 소매 및 전자상거래 등) 및 지역별로 분류되어 있습니다. 시장 예측은 금액(달러) 기준으로 제시되어 있습니다.
세계 소프트웨어 구성 분석 시장 동향 및 인사이트
오픈소스 구성 요소에 대한 의존도
오픈소스 라이브러리는 기업 코드베이스의 99% 이상에 존재하며, 레거시 용도 보안 도구로는 메울 수 없는 가시성의 격차를 초래하고 있습니다. 패키지 관리자 및 컨테이너 이미지는 간접적인 의존성을 증폭시키기 때문에 현재 평균적인 클라우드 네이티브 애플리케이션에는 여러 언어를 아우르는 수백 개의 타사 모듈이 통합되어 있습니다. 2024년, 주요 저장소에서 취약점이 있는 패키지나 악성 패키지가 28% 증가함에 따라 보안 팀은 지속적인 모니터링과 인벤토리 자동화를 도입할 수밖에 없게 되었습니다. 위험에 노출되어 있음에도 불구하고, 조직들은 오픈소스에 대한 의존을 유지하고 있습니다. 이는 오픈소스 활용으로 연간 개발 비용이 약 8조 8,000억 달러 절감되기 때문이며, 혁신 주도형 로드맵에서 오픈소스를 포기하는 것은 현실적이지 않기 때문입니다.
SBOM 및 규정 준수 관련 규제 요건
미국에서는 연방 정부 공급업체가 대통령령 제14028호 및 CISA(사이버보안·인프라보안국)가 2024년 3월에 제정한 ‘안전한 소프트웨어 개발 인증 프레임워크’에 따라 인증된 SBOM을 제출해야 합니다. 2024년 12월에 시행될 유럽연합(EU)의 ‘사이버 복원력 법’은 디지털 요소를 포함하는 모든 제품에 대해 SBOM 작성을 의무화하고, 위반 시 전 세계 매출액의 최대 2.5%에 해당하는 벌금을 부과한다고 명시하고 있습니다. 일본 경제산업성(METI)도 유사한 지침을 발표하여, 전 세계 정책 흐름이 일치해 가고 있음을 보여주고 있습니다. 규정 준수 요구에 따라, 소프트웨어 구성 분석(SCA)을 활용한 조달은 그동안 소프트웨어 보안이 부차적인 위치에 있던 제조, 자동차, 의료, 산업 자동화 분야로 확대되고 있습니다.
SCA에 정통한 인재 부족
미국에서만 해도 사이버 보안 인재 수요에 비해 22만 5,000명이 부족한 상황이며, 많은 조직이 상세한 의존성 그래프 해석, 취약점 우선순위 지정, 시정 조치 수립을 위한 전문 지식을 갖추지 못한 상태입니다. 소프트웨어 구성 분석은 개발, 법무, 조달 등 여러 부서에 걸쳐 있기 때문에 기존의 보안 인력 채용만으로는 이러한 기술 격차를 메울 수 없습니다. 기업에 따르면, 신규 분석가의 교육 기간은 6-12개월에 달하기 때문에 벤더의 전문 서비스나 관리형 보안 제공업체에 대한 의존도가 높아지고 있으며, 그 결과 총 소유 비용(TCO)이 증가하고 있습니다.
부문 분석
2025년에는 솔루션이 매출의 66.80%를 차지했습니다. 이는 기업이 취약점 감지, 라이선싱, SBOM 자동화를 단일 콘솔에 통합한 통합 제품군을 선호하는 경향을 반영합니다. 광범위한 정책 엔진, 개발자용 플러그인, 워크플로우 오케스트레이션 기능을 통해 중복되는 보안 기능의 통합이 촉진되고 있습니다. 서비스 부문은 규모는 작지만, 2031년까지 연평균 성장률(CAGR) 18.05%로 확대될 것으로 예측됩니다. 이는 대부분의 조직이 스캔 정책을 미세 조정하고, 광범위한 CI/CD 파이프라인에 도구를 통합하며, 미묘한 라이선싱 리스크를 해석하는 데 필요한 심도 있는 전문 지식이 부족하기 때문입니다. 따라서 컨설팅, 통합 및 관리형 감지 서비스는 기업이 플랫폼 투자를 운영화하는 데 도움이 됩니다.
다양한 언어로 구성된 수천 개의 리포지토리를 보유한 조직에서는 스캔 성능 맞춤 설정, 시정 조치 플레이북 설계, 그리고 결과를 거버넌스·리스크 및 컴플라이언스(GRC) 대시보드에 통합하기 위해 전문 서비스 파트너를 활용하는 경향이 강해지고 있습니다. 중견 기업의 구매자에게는 매니지드 서비스가 턴키 방식의 대시보드와 전문가의 트리아지를 제공함으로써 도입에 소요되는 시간을 단축시켜 줍니다. 그 결과, 플랫폼 이용료가 여전히 소프트웨어 구성 분석(SCA) 시장의 기반을 이루고 있음에도 불구하고, 서비스 매출의 성장률은 순수한 라이선스 확대를 상회하고 있습니다.
클라우드 호스팅형 제품은 2025년에 62.10%의 점유율을 차지하고 연평균 성장률(CAGR) 19.05%를 나타낼 것으로 전망되며, 이는 SaaS의 경제성이 애자일 소프트웨어 파이프라인과 어떻게 시너지를 창출하고 있는지를 여실히 보여줍니다. 데이터베이스의 즉각적인 업데이트, 탄력적인 컴퓨팅 용량, GitHub 및 GitLab 액션과의 직접 통합을 통해 전용 인프라 없이도 빈번한 스캔이 가능해집니다. On-Premise 배포는 데이터 주권 및 수출 관리 규제로 인해 외부로의 코드 이동이 제한되는 국방, 중요 인프라 및 규제가 엄격한 금융 기관에서 여전히 필수적입니다.
하이브리드 방식은 현실적인 중간 대안으로 부상하고 있으며, 기업은 기밀성이 높은 소스 코드를 로컬 스캐너에 보관하면서 클라우드 API를 통해 실시간 취약점 정보를 획득할 수 있게 됩니다. 각 벤더는 AI를 활용한 수정 제안, 모델 훈련에 클라우드 GPU 클러스터를 활용하는 컨테이너 이미지 스캔을 통해 차별화를 꾀하고 있습니다. 이러한 기술적 심화 덕분에 네이티브 SaaS 선도 기업과 기존의 On-Premise형 기업 간의 성능 격차가 확대되고 있으며, 예산 배분은 영구 라이선스보다 클라우드 구독 방식으로 전환되고 있습니다.
지역별 분석
북미는 2025년 매출의 27.10%를 차지하며, 여전히 가장 규모가 큰 지역 기여원으로 남아 있습니다. 이는 모든 정부 소프트웨어 계약업체에 SBOM 제출과 보안 개발 증명을 의무화하는 미국 연방 정부의 조달 요건에 힘입은 결과입니다. 이 지역은 탄탄한 벤처 캐피털 생태계, 성숙한 DevSecOps 문화, 그리고 민간 부문의 도입을 가속화하는 플랫폼 공급업체의 집중이라는 혜택을 누리고 있습니다.
유럽에서는 2024년 12월 ‘사이버 복원력 법(Cyber Resilience Act)’이 시행되어 2027년까지 EU 지역 내에서 판매되는 모든 디지털 제품에 대해 SBOM 제출이 의무화됨에 따라 성장세가 가속화되고 있습니다. 독일은 수출 지향적인 제조업 기반을 바탕으로 조기 도입을 주도하고 있는 반면, 영국은 금융 서비스 현대화 프로그램과 국가 인프라 강화 이니셔티브를 통해 지출의 모멘텀을 유지하고 있습니다.
아시아태평양은 2031년까지 연평균 성장률(CAGR)이 18.88%로 가장 높은 성장세를 보이고 있습니다. 일본은 경제산업성(METI)을 통해 상세한 SBOM 지침을 공표했으며, 현재 대기업으로 구성된 컨소시엄이 도입을 효율화하기 위한 공통 툴 스택의 시범 운영을 진행하고 있습니다. 중국은 전략적 산업을 보호하기 위해 국내 소프트웨어 구성 분석(SCA) 역량에 대한 투자를 추진하고 있는 반면, 인도의 IT 서비스 업계에서는 다국적 기업과의 계약에 SBOM 작성을 포함시키고 있습니다. 동남아시아 국가들에서는 공공 부문의 디지털화 추진으로 인해 공급망상의 위협에 노출되는 사례가 증가하고 있으며, 예방적 대책이 요구됨에 따라 이에 대한 관심이 높아지고 있습니다.
기타 혜택:
- 엑셀 형식 시장 예측(ME) 시트
- 3개월간 애널리스트 지원
자주 묻는 질문
목차
제1장 서론
제2장 조사 방법
제3장 주요 요약
제4장 시장 구도
제5장 시장 규모와 성장 예측
제6장 경쟁 구도
제7장 시장 기회와 향후 전망
LSH 26.09.14According to Mordor Intelligence, the software composition analysis market size was valued at USD 364.69 billion in 2025 and estimated to grow from USD 430.12 billion in 2026 to reach USD 981.62 billion by 2031, at a CAGR of 17.95% during the forecast period (2026-2031).
This report is Segmented by Component (Solutions, Services), Deployment Mode (Cloud, On-Premises, Hybrid), Organization Size (Large Enterprises, Small and Medium Enterprises), Industry Vertical (IT and Telecom, BFSI, Retail and E-Commerce, and More), and by Geography. The Market Forecasts are Provided in Terms of Value (USD).
Global Software Composition Analysis Market Trends and Insights
Dependence on Open-Source Components
Open-source libraries appear in more than 99% of enterprise codebases, creating visibility gaps that legacy application security tooling cannot bridge. Package managers and container images multiply transitive dependencies, so an average cloud-native application now incorporates hundreds of third-party modules across several languages. Vulnerable or malicious packages grew 28% in major repositories during 2024, forcing security teams to adopt continuous monitoring and inventory automation. Despite risk exposure, organizations retain open-source reliance because it saves an estimated USD 8.8 trillion in annual development costs, making abandonment impractical for innovation-driven roadmaps.
Regulatory Mandates for SBOM and Compliance
In the United States, federal suppliers must now deliver attested SBOMs under Executive Order 14028 and CISA's March 2024 Secure Software Development Attestation framework.The European Union's Cyber Resilience Act, effective December 2024, obliges SBOM creation for every product with digital elements and imposes penalties of up to 2.5% of global turnover for non-compliance. Japan's Ministry of Economy, Trade and Industry (METI) has issued similar guidelines, signaling converging global policy momentum. Compliance imperatives extend Software Composition Analysis procurement into manufacturing, automotive, healthcare, and industrial automation domains where software security was previously peripheral.
Shortage of SCA-Skilled Talent
The United States alone trails demand by 225,000 cybersecurity workers, leaving many organizations without the expertise to interpret detailed dependency graphs, prioritize vulnerabilities, and craft remediation policies. Because Software Composition Analysis spans development, legal, and procurement functions, the skills gap cannot be bridged through traditional security hiring alone. Firms report six-to-twelve-month onboarding cycles for new analysts, driving reliance on vendor professional services and managed security providers, which elevates total cost of ownership.
Other drivers and restraints analyzed in the detailed report include:
- Escalating Supply-Chain Cyber-attacks
- Shift-Left DevSecOps Budgets
- High False-Positive Fatigue
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
Solutions generated 66.80% revenue in 2025, reflecting enterprise preference for unified suites that combine vulnerability detection, license governance, and SBOM automation in a single console. Extensive policy engines, developer plug-ins, and workflow orchestration capabilities encourage consolidation of overlapping security functions. Services, though smaller, accelerate at 18.05% CAGR through 2031 because most organizations lack deep expertise to fine-tune scan policies, embed tooling into sprawling CI/CD pipelines, and interpret nuanced license risks. Consulting, integration, and managed detection offerings therefore help enterprises operationalize platform investments.
Organizations with thousands of repositories across diverse languages increasingly engage specialist service partners to customize scan performance, design remediation playbooks, and integrate results into governance, risk, and compliance dashboards. For mid-market buyers, managed services offset onboarding time by providing turnkey dashboards and expert triage. As a result, services revenue growth outpaces pure license expansion, even though platform fees continue to anchor the Software Composition Analysis market.
Cloud-hosted products secured 62.10% share in 2025 and display a 19.05% CAGR outlook, underscoring how SaaS economics resonate with agile software pipelines. Instant database updates, elastic compute capacity, and direct integration with GitHub or GitLab actions enable high-frequency scans without dedicated infrastructure. On-premises deployments remain essential in defense, critical infrastructure, and highly regulated financial institutions where data sovereignty or export-control rules prevent external code movement.
Hybrid patterns emerge as a pragmatic middle path, allowing enterprises to retain sensitive source code in local scanners while pulling real-time vulnerability intelligence from cloud APIs. Vendors differentiate through AI-supported remediation suggestions and container image scanning that leverage cloud GPU clusters for model training. This technical depth widens the performance gap between native-SaaS leaders and legacy on-premise incumbents, steering budget allocations toward cloud subscriptions over perpetual licenses.
Complete Report Scope:
- By Component
- Solutions
- Services
- By Deployment Mode
- Cloud
- On-premises
- Hybrid
- By Organisation Size
- Large Enterprises
- Small and Medium Enterprises
- By Industry Vertical
- IT and Telecom
- BFSI
- Retail and E-commerce
- Government
- Healthcare and Life Sciences
- Manufacturing
- Automotive
- Energy and Utilities
- Other Verticals
- By Geography
- North America
- United States
- Canada
- Mexico
- South America
- Brazil
- Argentina
- Rest of South America
- Europe
- Germany
- United Kingdom
- France
- Italy
- Spain
- Rest of Europe
- Asia-Pacific
- China
- Japan
- India
- South Korea
- Southeast Asia
- Rest of Asia-Pacific
- Middle East and Africa
- Middle East
- Saudi Arabia
- United Arab Emirates
- Turkey
- Rest of Middle East
- Africa
- South Africa
- Nigeria
- Egypt
- Rest of Africa
- Middle East
- North America
Geography Analysis
North America remained the largest regional contributor with 27.10% of 2025 revenue, anchored by U.S. federal procurement mandates that oblige every government software contractor to furnish SBOMs and secure-development attestations. The region benefits from deep venture-capital ecosystems, mature DevSecOps cultures, and a concentration of platform vendors that accelerate private-sector adoption.
Europe's trajectory strengthens following the December 2024 enactment of the Cyber Resilience Act, which obliges SBOMs for any digital product sold in the bloc by 2027. Germany drives early uptake thanks to its export-oriented manufacturing base, while the United Kingdom maintains spending momentum through financial-services modernization programs and national infrastructure hardening initiatives.
Asia-Pacific posts the fastest 18.88% CAGR through 2031. Japan promulgated detailed SBOM guidelines via METI, and a consortium of major enterprises now pilots common tooling stacks to streamline adoption. China invests in domestic Software Composition Analysis capacity to protect strategic industries, whereas India's IT-services sector embeds SBOM generation into contracts with multinational customers. Southeast Asian economies show rising interest as public-sector digitalization initiatives expose them to supply-chain threats that demand proactive controls.
- Synopsys Inc.
- Sonatype Inc.
- Snyk Ltd.
- Veracode Inc.
- Mend.io (White Source Ltd.)
- Flexera (Revenera)
- Contrast Security Inc.
- OpenText Corp.
- Perforce Software Inc.
- Checkmarx Ltd.
- GitLab Inc.
- GitHub (Microsoft Corp.)
- JFrog Ltd.
- Black Duck (Synopsys)
- Endor Labs
- Datadog Inc.
- Palo Alto Networks (Prisma Cloud)
- IBM Corp.
- Broadcom (Symantec)
- Micro Focus (OpenText)
- nexB Inc.
- Qwiet AI
- SecureStack
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Study Assumptions and Market Definition
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Market Drivers
- 4.2.1 Dependence on Open-Source Components
- 4.2.2 Regulatory Mandates for SBOM and Compliance
- 4.2.3 Escalating Supply-Chain Cyber-attacks
- 4.2.4 Shift-Left DevSecOps Budgets
- 4.2.5 Cyber-insurance Underwriting Requirements
- 4.2.6 AI Code-Generation Expanding Transitive Dependencies
- 4.3 Market Restraints
- 4.3.1 Shortage of SCA-Skilled Talent
- 4.3.2 High False-Positive Fatigue
- 4.3.3 License Fatigue Curtailing Scan Scope
- 4.3.4 Run-time Integrity Tools Cannibalising SCA Spend
- 4.4 Supply-Chain Analysis
- 4.5 Regulatory Landscape
- 4.6 Technological Outlook
- 4.7 Porter's Five Forces
- 4.7.1 Bargaining Power of Buyers
- 4.7.2 Bargaining Power of Suppliers
- 4.7.3 Threat of New Entrants
- 4.7.4 Threat of Substitutes
- 4.7.5 Intensity of Competitive Rivalry
- 4.8 Assesment of Macroeconomic Factors on the market
5 MARKET SIZE AND GROWTH FORECASTS (VALUE)
- 5.1 By Component
- 5.1.1 Solutions
- 5.1.2 Services
- 5.2 By Deployment Mode
- 5.2.1 Cloud
- 5.2.2 On-premises
- 5.2.3 Hybrid
- 5.3 By Organisation Size
- 5.3.1 Large Enterprises
- 5.3.2 Small and Medium Enterprises
- 5.4 By Industry Vertical
- 5.4.1 IT and Telecom
- 5.4.2 BFSI
- 5.4.3 Retail and E-commerce
- 5.4.4 Government
- 5.4.5 Healthcare and Life Sciences
- 5.4.6 Manufacturing
- 5.4.7 Automotive
- 5.4.8 Energy and Utilities
- 5.4.9 Other Verticals
- 5.5 By Geography
- 5.5.1 North America
- 5.5.1.1 United States
- 5.5.1.2 Canada
- 5.5.1.3 Mexico
- 5.5.2 South America
- 5.5.2.1 Brazil
- 5.5.2.2 Argentina
- 5.5.2.3 Rest of South America
- 5.5.3 Europe
- 5.5.3.1 Germany
- 5.5.3.2 United Kingdom
- 5.5.3.3 France
- 5.5.3.4 Italy
- 5.5.3.5 Spain
- 5.5.3.6 Rest of Europe
- 5.5.4 Asia-Pacific
- 5.5.4.1 China
- 5.5.4.2 Japan
- 5.5.4.3 India
- 5.5.4.4 South Korea
- 5.5.4.5 Southeast Asia
- 5.5.4.6 Rest of Asia-Pacific
- 5.5.5 Middle East and Africa
- 5.5.5.1 Middle East
- 5.5.5.1.1 Saudi Arabia
- 5.5.5.1.2 United Arab Emirates
- 5.5.5.1.3 Turkey
- 5.5.5.1.4 Rest of Middle East
- 5.5.5.2 Africa
- 5.5.5.2.1 South Africa
- 5.5.5.2.2 Nigeria
- 5.5.5.2.3 Egypt
- 5.5.5.2.4 Rest of Africa
- 5.5.5.1 Middle East
- 5.5.1 North America
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global-level Overview, Market-level Overview, Core Segments, Financials, Strategic Information, Market Rank/Share, Products and Services, Recent Developments)
- 6.4.1 Synopsys Inc.
- 6.4.2 Sonatype Inc.
- 6.4.3 Snyk Ltd.
- 6.4.4 Veracode Inc.
- 6.4.5 Mend.io (White Source Ltd.)
- 6.4.6 Flexera (Revenera)
- 6.4.7 Contrast Security Inc.
- 6.4.8 OpenText Corp.
- 6.4.9 Perforce Software Inc.
- 6.4.10 Checkmarx Ltd.
- 6.4.11 GitLab Inc.
- 6.4.12 GitHub (Microsoft Corp.)
- 6.4.13 JFrog Ltd.
- 6.4.14 Black Duck (Synopsys)
- 6.4.15 Endor Labs
- 6.4.16 Datadog Inc.
- 6.4.17 Palo Alto Networks (Prisma Cloud)
- 6.4.18 IBM Corp.
- 6.4.19 Broadcom (Symantec)
- 6.4.20 Micro Focus (OpenText)
- 6.4.21 nexB Inc.
- 6.4.22 Qwiet AI
- 6.4.23 SecureStack
7 MARKET OPPORTUNITIES AND FUTURE OUTLOOK
- 7.1 White-Space and Unmet-Need Assessment


